
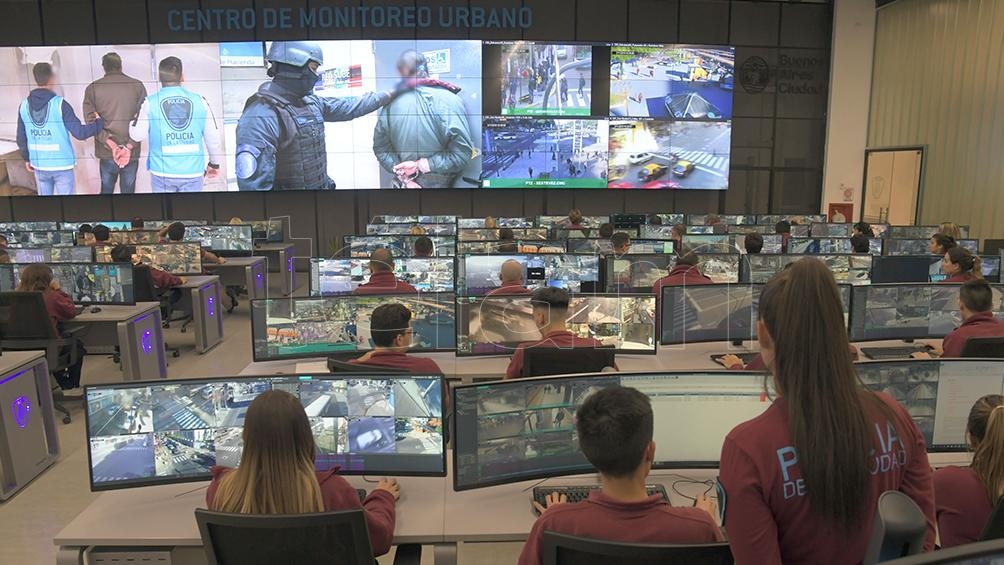
The Government of the Autonomous City of Buenos Aires is once again pushing for the deployment of facial recognition systems in public spaces. Fundación Vía Libre, acting as amicus curiae (Friend of the Court), has filed a new motion in the lawsuit titled “O.D.I.A. y Otros c/ G.C.B.A. s/ amparo” to present our observations on the bidding terms and conditions for a new facial recognition and video-based alert management service under a Framework Agreement (Orden de Compra Abierta) issued by the City Government.
The document we submitted is available here:
It is important to recall that the courts ordered the suspension of the Facial Recognition System until three key conditions were met: 1) the establishment and proper functioning of oversight bodies; 2) the execution of necessary studies and testing on the software to determine whether its use has a discriminatory impact based on personal characteristics; and 3) full public disclosure and transparency to requesting residents and organizations regarding the tool’s existence, operation, and governing legal framework.
The truth is that the second requirement stalled due to the impossibility of auditing the system’s operation, as neither the source code nor other relevant technical data were submitted to the case file. Under these circumstances, the City Government is attempting to procure a new system and has submitted the bidding terms to the court for review.
Our observations on these bidding terms have already been filed, and the court must now evaluate the proposal before deciding whether to authorize the procurement of a new system in the City of Buenos Aires.
From Fundación Vía Libre, we would like to highlight several key concerns:
a) Imprecise specifications and serious omissions: The Technical Specifications Document (PET, by its Spanish acronym) contains vague and inaccurate details. It fails to outline any method for evaluating or mitigating bias—a core requirement mandated by the court.
b) Absence of essential operational elements: Critical technical details are missing from the document. Expert witness Sebastián Uchitel clearly explained that it is impossible to assess whether the system is secure without contextual information on how it will be implemented.
c) An audit that excludes the core algorithm: The audit outlined in the PET does not cover the system’s algorithmic engine. The document only requires a sworn declaration from the successful bidder and a commitment letter from the vendor agreeing to grant access to the software code for data integration processes in case of “legal contingencies or IT security requirements.”
This raises two major issues: first, accessing the code is treated as an exception triggered by contingencies rather than a standard rule ensuring the auditability required by lower and appellate court rulings; second, the source code of the AI engine—and consequently access to the training datasets and performance metrics across demographic subgroups—is completely excluded from this commitment.
Furthermore, it is deeply concerning that the PET assigns the responsibility for auditing the overall system to the winning contractor under a lenient sworn statement with minimal obligations. The bidding document also fails to specify who will review the audit submitted by the vendor.
As emphasized in our filing:
“Surrendering the source code should be a binding contractual obligation set forth in the bidding rules. It must apply to the algorithmic engine, detailing the training datasets used and how target demographics are represented—factors that directly impact inherent system bias. Unless clear conditions are established, the system will remain practically impossible to audit.”
It is also worth noting that the bidding terms fail to guarantee personal data protection or establish sufficient institutional controls. To make matters worse, the City Ministry of Security grants itself the power to authorize the vendor to use personal data for retraining its systems.
The bidding text explicitly states that “the information and data accessed by the contractor may not be reused or employed for training, fine-tuning, validating, developing, or improving artificial intelligence systems or models without prior express authorization from the MSEGC.” It cannot be stressed enough that biometric personal data is sensitive data, and the City Government lacks the legal authority to permit a private company to use citizens’ data under any circumstances.
Finally, we submitted a set of baseline guidelines for Privacy Impact Assessments regarding facial recognition systems. We believe these guidelines must be mandatory when procuring any service of this nature, given its potential to infringe upon the fundamental rights of the general public—regardless of efforts to locate fugitives or any other public safety justification that may be claimed.